ResolverFuzz: fuzzing DNS resolvers with query-response pairs
Updated September 21, 2026
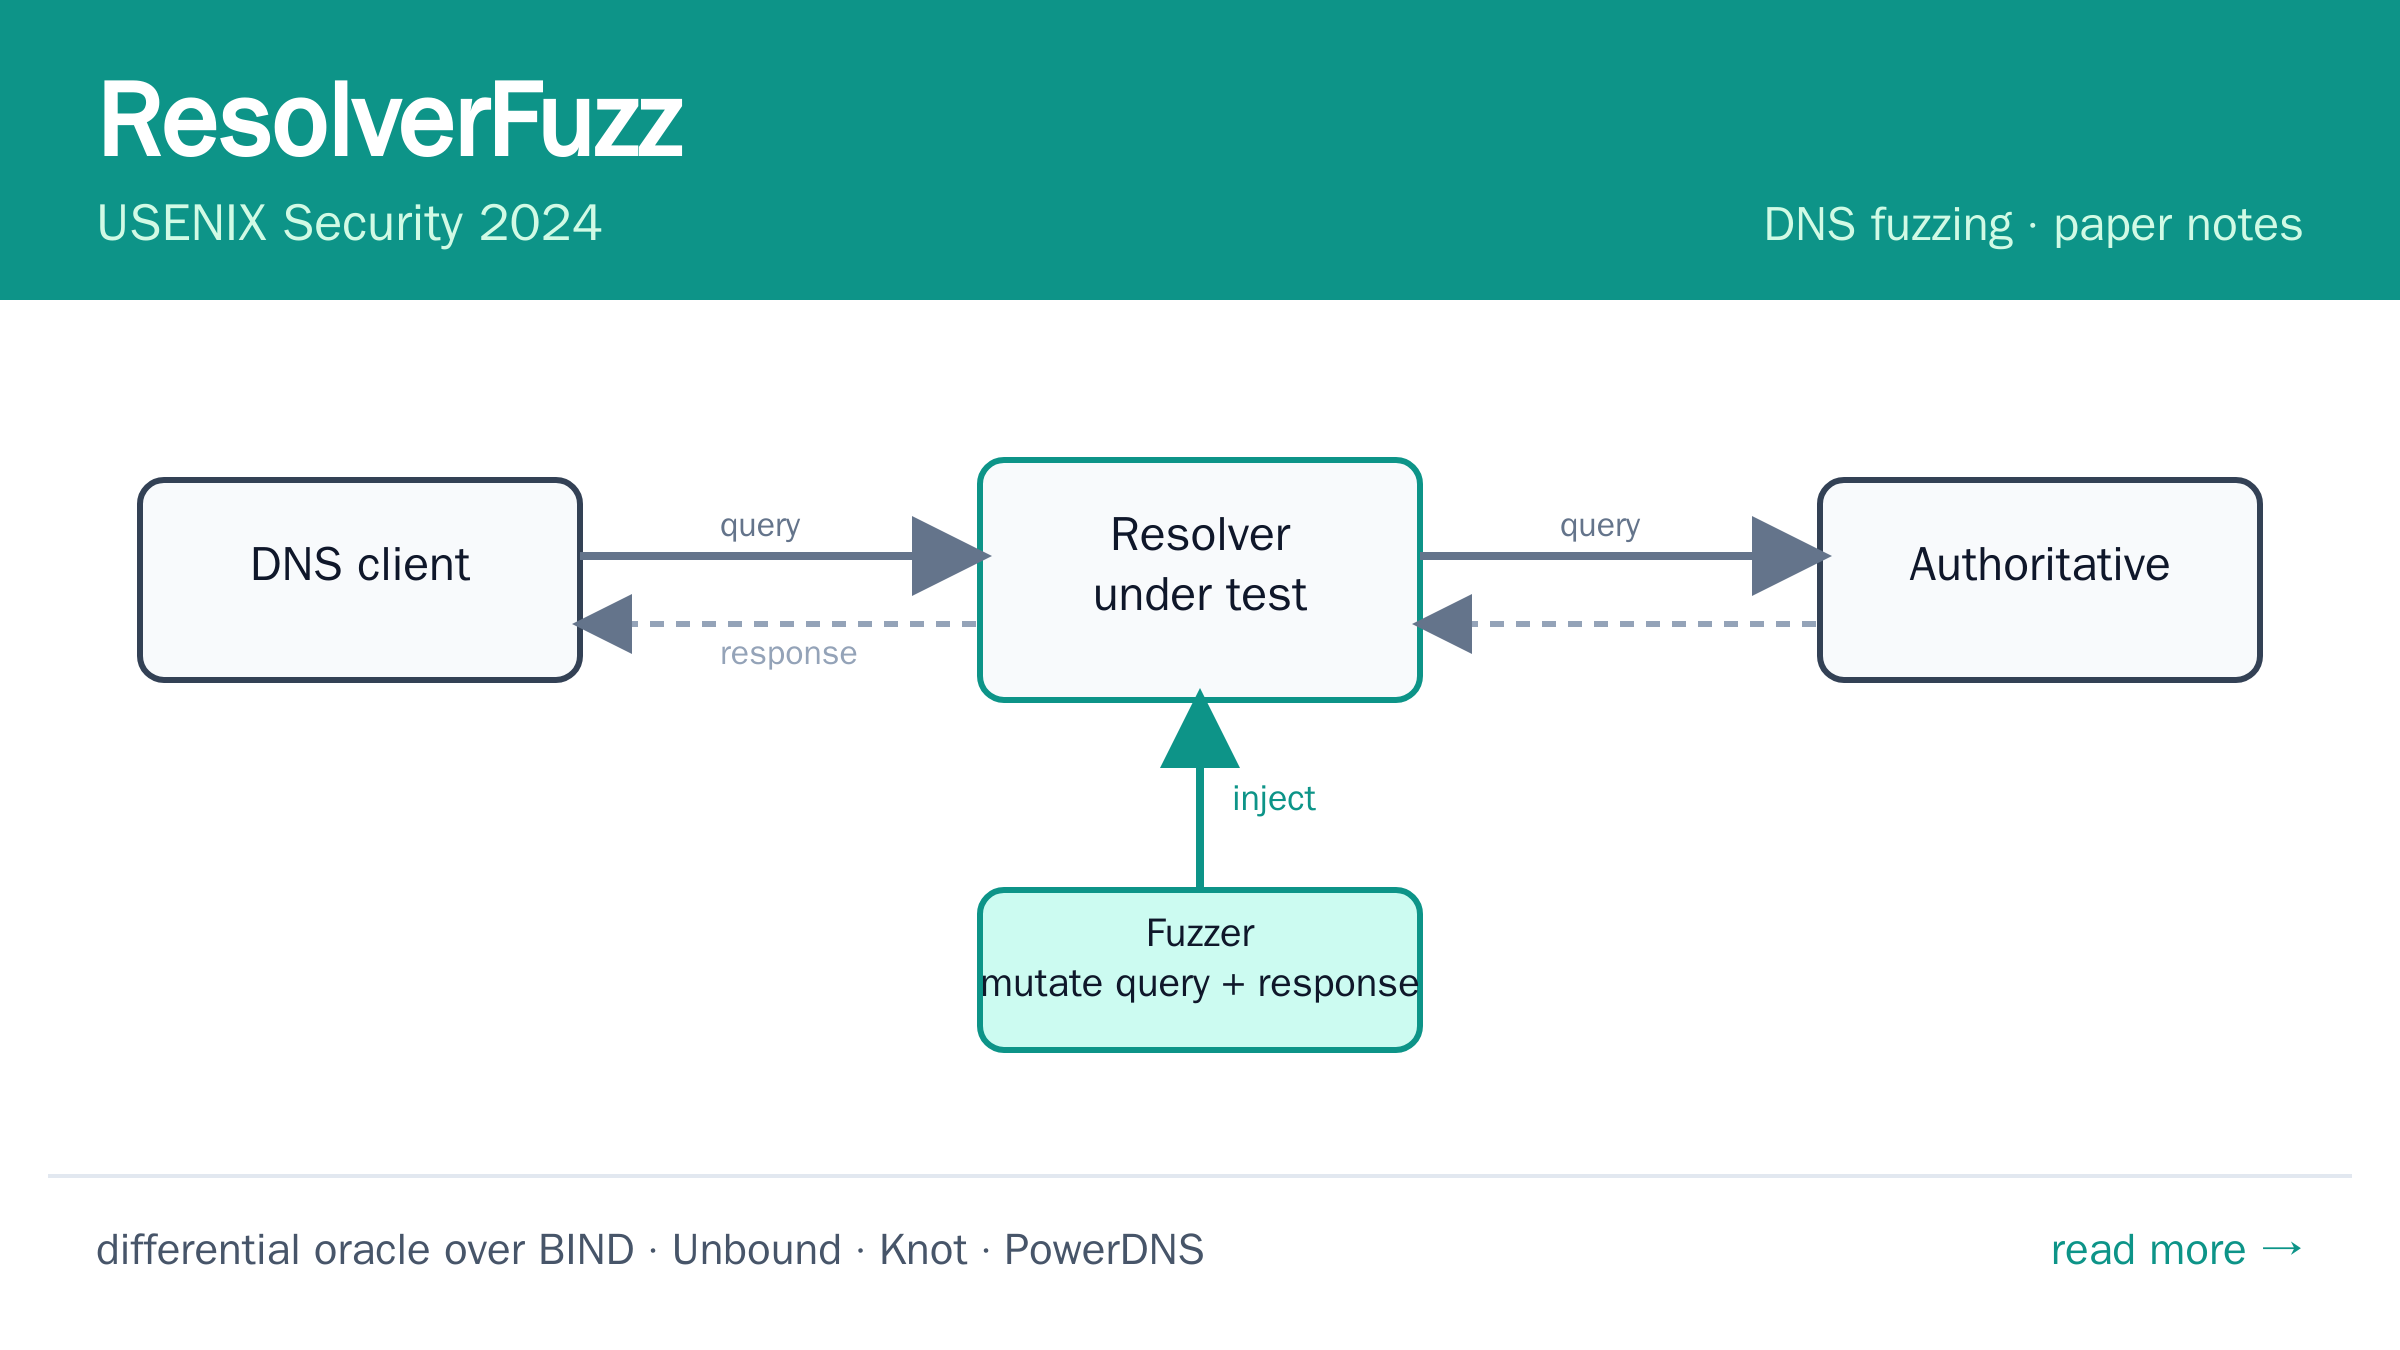
ResolverFuzz goes after the resolver — the stateful, cache-holding middle of DNS that most fuzzers skip. It drives a resolver under test inside a controlled client-resolver-authoritative loop, mutating both the client's query and the authoritative response, then leans on differential testing across BIND, Unbound, Knot Resolver and PowerDNS to flag divergent behaviour. The payoff is cache-poisoning, resource-exhaustion and crash bugs that only show up once a resolver's cross-request state is exercised.
I spent a weekend pointing a cut-down version at a local Unbound build and it turned up a caching inconsistency faster than I expected — the real contribution here is the harness and the client/resolver/auth setup, not any single bug. It's a good reminder that the interesting DNS bugs live in state, not in a single packet parser.
Paper: USENIX Security 2024
712 views